Skip to content
OQVIAN

Access control, secret scanning, and incident containment.

We lock down cloud IAM, block exposed credentials before they ship, and wire your alerts into repeatable containment playbooks.

Test policy rules and incident containment.

Inspect how incoming requests, credential checks, and containment playbooks behave in a simulated environment.

Demo

Simulated with sample data. Not a live system.

Ingest and analyze telemetry for anomalous behavior.

142 events/secSimulated

Notification center

Illustrative security feed

Sample

Sign-in challenged

Unrecognized source, MFA required

All notifications shown here are sample content and are not connected to a live alert system.

Security controls around every layer

A visual map of common defensive practices from identity and code review through monitoring and response.

TRUST
Select a protection boundary

Identity & access

Access is granted to verified identities with scoped permissions.

Tools & building blocks

  • IAM
  • MFA
  • Least privilege

Illustrative control categories. Security products are selected after scope, risk, and environment are reviewed.

Automated gates in the commit and deploy loop.

Illustrative terminal log showing pre-commit secret scanning, container CVE checks, and bucket access enforcement.

➜ git commit -m "update config"
[pre-commit] Scanning for exposed secrets… blocked
AWS Access Key found in line 12. Commit rejected.
➜ trigger build-pipeline
[pipeline] Running container vulnerability gates… passed
Illustrative result: no Critical or High vulnerabilities detected.
➜ monitor cloud-config
WARN: S3 bucket 'app-data-prod' public access drift detected.
[auto-remediation] Enforcing Block Public Access… complete

From manual log checks to automated enforcement.

How credential handling and incident response change when security rules run automatically on every commit and alert.

BeforeManual reviews & shared keys
  1. 01Shared keysLong-lived API tokens pasted into repo files
  2. 02Broad IAMServices run with admin access to every table
  3. 03Alert floodsRepeated ping failures bury real security signals
  4. 04Late reviewAudits happen months after code is in production
AfterAutomated gates & scoped access
  1. 01Pre-commit blockExposed secrets reject the commit before push
  2. 02Scoped rolesEach worker gets least-privilege tokens per task
  3. 03One incidentCorrelated alerts open a single tracked ticket
  4. 04Auto-containSuspicious tokens are revoked and logged immediately

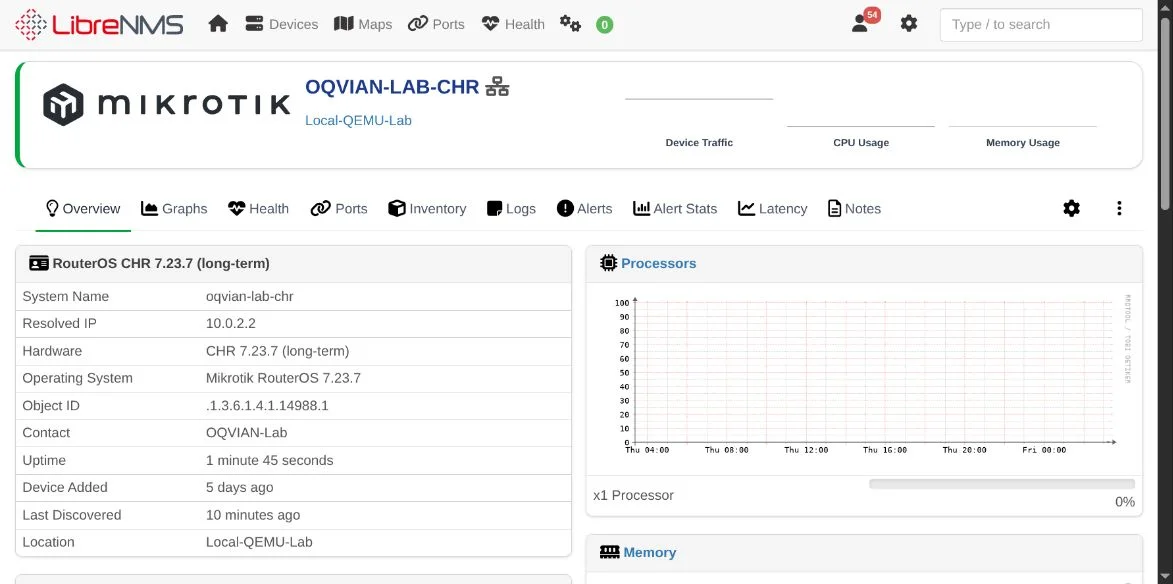
Outage detection to closed incident in our lab.

In our network alert lab built for Jackson Electric Cooperative, a simulated router outage triggers a health failure, deduplicates repeated alerts into one tracked incident, and records recovery when the device comes back online.
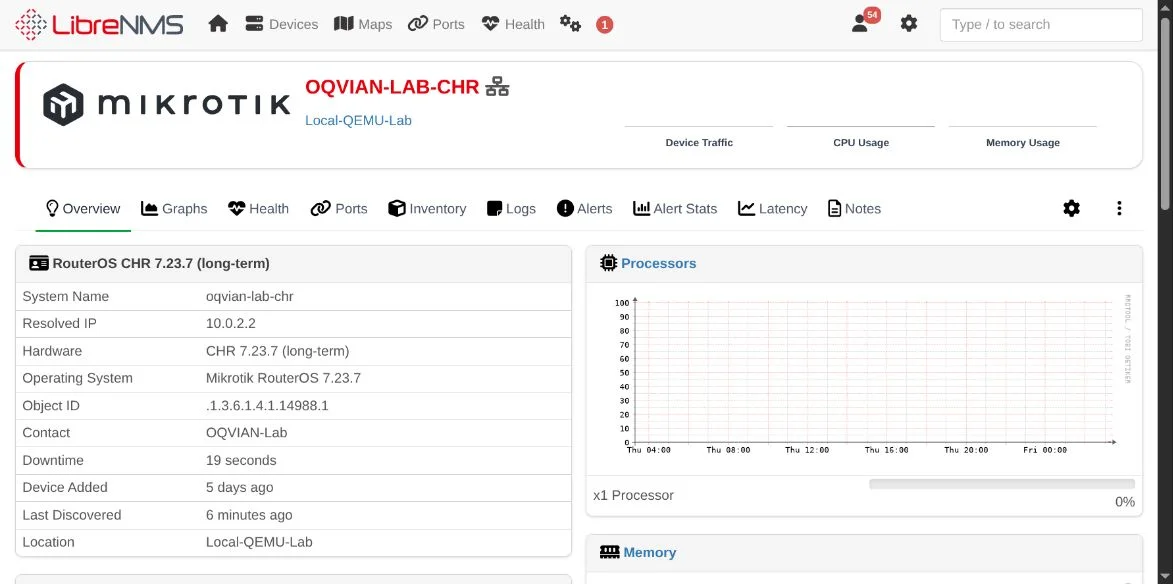
Alert lab showing router outage and open incident
1. Outage detected & incident openedRepeated ping failures are grouped into a single tracked incident so operators are not flooded with duplicate pages.
Alert lab showing router recovery and resolved incident
2. Recovery verified & loggedWhen the link responds again, the workflow marks the incident resolved and preserves the timestamped log.

Hardening across cloud, web apps, and automations.

We review IAM roles, webhook signatures, and network boundaries across every system we build or audit.

See the full workflow diagram on Automate

Common questions

Need a security review or alert workflow?

Talk with our security engineer to review your cloud permissions, webhook keys, or incident response setup.

Request a security review